Waratek Waratek Security Newsletter

All issues

The newest is an Apache Axis flaw published on 6 November. A Waratek rule blocks exploitation of 4 of the 6.
 
Waratek Security Newsletter
No. 1 · 6 to 13 November 2026
In this issue
New report State of Java Exploits 2026
6 flaws attacked Apache Kylin, OS command injection through a REST API, Apache Axis, SOAP fault deserialization
3 products to check Apache Axis, Apache Axis2/Java, Keycloak
4 new Waratek patches in the last 30 days

Attacks were first recorded on 6 Java flaws, one of them published this week

Attacks were first recorded on 12 November on an Apache Axis flaw published 6 days earlier. It lets an unauthenticated caller make Axis load and create a class named in a SOAP fault, and the project marked it unsupported when the CVE was assigned. Five older flaws in Apache Kylin, Apache Shiro, Apache Struts and Red Hat JBoss EAP also have their first attack evidence dated this week.

A Waratek rule blocks exploitation of the Axis flaw and of the older flaws in Apache Kylin and Red Hat JBoss EAP.
 
 
New report

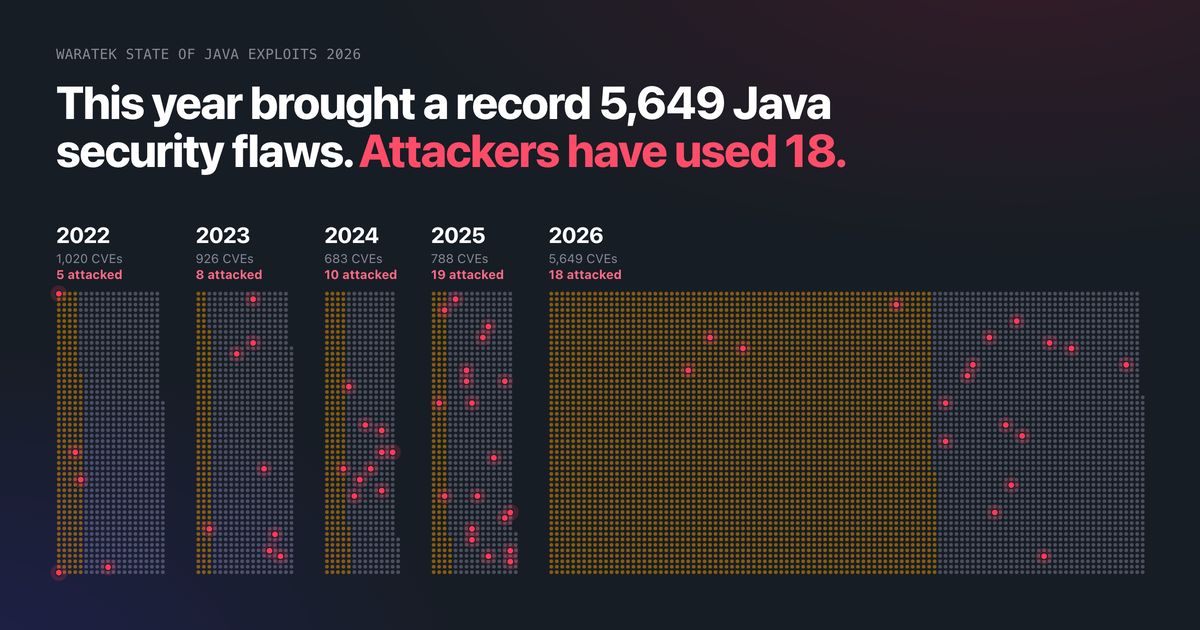
State of Java Exploits 2026

Attackers exploit a small and familiar set of flaws: ones with public exploit code, in a few kinds of bug, from a short list of projects, and often years old.

Read the report
 
100 ▼ 12
new Java CVEs
6
rated Critical
12
protected by Waratek, about 1 in 8
Source: VRT, the CVEs it tracks as Java, published 6 to 13 November 2026.
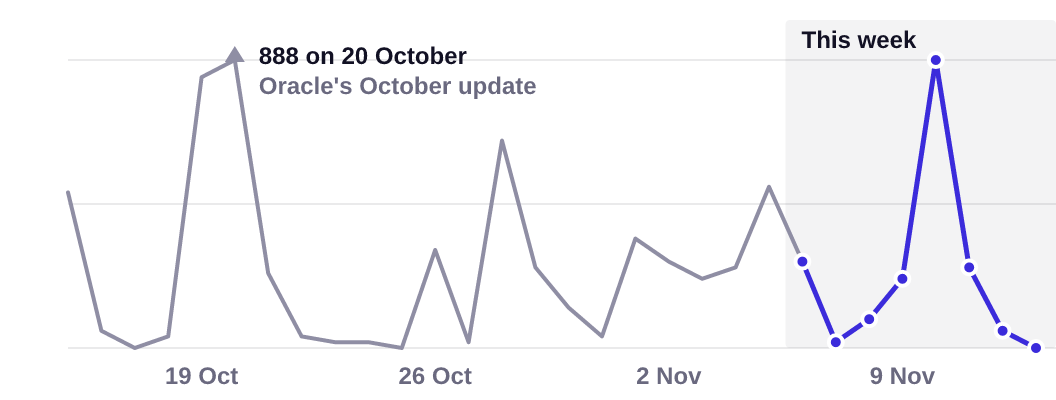
New Java CVEs per day, last 30 days
The tall bar on 20 October is Oracle's Critical Patch Update, with 888 flaws in one day. This week's busiest day was Tuesday 10 November, with 50.
New Java CVEs per day from 15 October 2026 to 13 November 2026. This week ran between 0 and 50 a day.
This week's 100 by severity
     
■ 6 Critical ■ 13 High ■ 29 Medium ■ 1 Low ■ 51 Not scored


Attacks were first recorded on 6 Java flaws this week

The earliest attack evidence for each, from CISA KEV and VulnCheck KEV, is dated between 8 and 12 November. A Waratek rule blocks exploitation of 4 of them.

Apache Kylin, OS command injection through a REST API
CVE-2020-13925 · published 14 July 2020 · attack evidence dated 12 November
Attacks were first recorded 6 years after publication.
■ Protected by Waratek
Apache Axis, SOAP fault deserialization
CVE-2026-90436 · published 6 November 2026 · attack evidence dated 12 November
Attacks were first recorded 6 days after publication.
■ Protected by Waratek
Apache Shiro, authentication bypass when used with Spring
CVE-2020-17523 · published 3 February 2021 · attack evidence dated 10 November
Attacks were first recorded on 10 November.
No Waratek rule
Apache Struts, ParameterInterceptor bypass
CVE-2011-3923 · published 1 November 2019 · attack evidence dated 9 November
Attacks were first recorded on 9 November.
No Waratek rule
Apache Struts, OGNL code in a redirect parameter
CVE-2013-1965 · published 10 July 2013 · attack evidence dated 8 November
Attacks were first recorded 13 years after publication.
■ Protected by Waratek
Red Hat JBoss EAP, RichFaces resource handling
CVE-2013-2165 · published 23 July 2013 · attack evidence dated 8 November
Attacks were first recorded on 8 November.
■ Protected by Waratek
Source: CISA KEV, VulnCheck KEV. The date is the earliest attack evidence either records.


Attacks were first recorded on an Apache Axis flaw 6 days after it was published

Apache Axis2/Java and Keycloak also had flaws rated Critical among this week's new ones.

Top scoreProductWaratek
9.8
1 new flaw · 1 Critical · 1 attacked
The project marked its new flaw unsupported, and attacks on it were first recorded on 12 November.
■ Protected by Waratek
9.1
7 new flaws · 2 Critical
It had 7 new flaws this week, and a Waratek rule blocks exploitation of the XML external entity flaw.
■ 1 of 7 protected
9.1
14 new flaws · 1 Critical
It had 14 new flaws this week, and the client management flaw was rated Critical.
No Waratek rule


Waratek added 4 patches in the last 30 days

Two were added this week, for SnakeYAML and Oracle Application Object Library. A patch blocks exploitation in the running application while an upgrade is planned.

9.8
Oracle Application Object Library, unauthenticated takeover over HTTP
CVE-2026-101767 · rated Critical
Public detail comes from Oracle's Critical Patch Update October 2026 advisory.
Added 12 November
9.8
SnakeYAML, unsafe deserialization in Constructor
CVE-2022-1471 · rated Critical
The patch was added on 10 November.
Added 10 November
8.1
Jolokia Webarchive Agent, JNDI injection in proxy mode
CVE-2018-1000130 · rated High
Added 5 November
9.8
Apache ShenYu, JWT authentication bypass in Admin
CVE-2021-37580 · rated Critical
Added 3 November
Waratek
If this would be useful to someone you know, send them this link to subscribe: java-weekly.news.waratek.com
 

Get this by email every week